
Trusted supply chains are becoming law
On 20 January 2026 the European Commission proposed a revised Cybersecurity Act (CSA 2.0) that creates a trusted ICT supply chain security framework for the first time: high-risk suppliers are identified on technical and non-technical grounds across 18 critical sectors and can be excluded from procurement of key ICT assets, EU funding and EU cybersecurity certification. The proposal is now going through the European Parliament and Council.
The US is tightening in parallel, from chip exports and outbound investment to AI regulation.
- 2027.01.01TISAX: assessments ordered from this date use VDA ISA2027, now released annually
- 2027.01.20EU Machinery Regulation (EU) 2023/1230 applies
- Model year 2027US connected vehicle rule: vehicles with Chinese- or Russian-linked software prohibited, hardware from model year 2030; an approved supplier registry was added in June 2026
- 2027.12.02EU AI Act obligations for standalone high-risk AI systems apply
- 2027.12.11The EU Cyber Resilience Act fully applies; digital products must demonstrate cybersecurity to carry CE marking
- 2027.12.23US federal procurement ban on certain Chinese semiconductors (NDAA Section 5949)
Gartner also predicts that by 2027 AI governance will become a requirement of sovereign AI laws. Suppliers that can be verified as trustworthy will stay on international customers’ lists in 2027.
Sources: European Parliament Legislative Observatory 2026/0011(COD); US Department of Commerce BIS; US Department of the Treasury; US Congress (congress.gov); US Federal Register; Official Journal of the EU; Gartner press release, 17 February 2025 (research forecast).
The EU and the US are writing trust into law
Only suppliers that can prove their products are secure, and show where they come from and where they go, will stay on international customers’ lists.
Support for every decision-maker
International regulation means something different to a CEO, CISO, CRO, CFO, CTO, product manager, general counsel and CHRO. See how Winners supports your role.
Turn compliance evidence into an edge for winning European orders
- Your concern
- Customer audits, export-market regulations and governance requirements arrive at once, and priorities must be set within a limited budget.
- Our approach
- We combine the requirements across our eight services into one roadmap: sequence, shared evidence, and which customer or market each investment serves.
- What you get
- A decision basis for your management meeting: applicable requirements, priorities and budget structure.
Answer ISO 27001, TISAX, CRA and GDPR with one body of evidence
- Your concern
- Each framework asks for its own audit evidence, incident reporting deadlines keep shrinking, and the team spends its time on paperwork.
- Our approach
- We map one set of controls to multiple requirements and define each process clearly: who is responsible, what is done, when, and where the evidence of doing it — or not — is kept.
- What you get
- A control-to-evidence map and a reporting procedure you can actually exercise.
Let the board make decisions on the basis of risk reports
- Your concern
- Risk information arrives in different formats, governance and disclosure expectations grow more specific, and the committee struggles to see priorities.
- Our approach
- We establish risk appetite, three lines and board reporting under ISO 31000 and COSO ERM, tracked with key risk indicators.
- What you get
- A risk reporting structure the board can decide on.
Tie every compliance investment to disclosure, evaluation and markets
- Your concern
- Financial reports must be signed and answered for, the annual report must disclose cybersecurity and integrity management, sustainability information is now a mandatory internal control audit item, and EU penalties and the compliance budget must be weighed at the same time.
- Our approach
- We integrate the evidence of each management system along the internal control finance cycles, sustainability information controls (COSO ICSR) and annual report disclosure requirements, and turn EU penalties and TWSE ESG evaluation bonus points into a basis for investment decisions.
- What you get
- A compliance investment plan for the board: applicable requirements, budget structure, disclosure mapping and sustainability information control points.
Build secure design and R&D protection into the development process you already have
- Your concern
- The R&D cycle of internal control, trade secret protection and the EU CRA secure design requirements arrive together, and the R&D team needs an approach that does not start a second process.
- Our approach
- We add CRA secure design, IEC 62443-4-1, ISO/SAE 21434 and trade secret protection incrementally to your existing development framework (such as ASPICE or ISO 26262), with R&D records and technical documentation kept under one set of rules.
- What you get
- A map of requirements to each gate of the R&D process, and protection for R&D output.
Confirm the CRA class and assessment route for each product line
- Your concern
- CRA and AI Act requirements must enter the development schedule, and product classes and the obligations of own-brand, ODM and OEM roles need clarifying first.
- Our approach
- We determine CRA class and supply-chain role per product line and build secure design, SBOM and vulnerability handling into development; six companies are currently in CRA advisory with Winners.
- What you get
- An assessment route for each product line and the scope of technical documentation to prepare.
Make contract terms, regulatory investigations and the compliance programme hold up
- Your concern
- Customers ask for more security, data, AI and anti-bribery clauses, and regulatory investigations, cross-border legal conflicts and evidence preservation after incidents all need preparing in advance.
- Our approach
- We turn the obligations in each regulation and customer clause into an auditable system and records, so that in an incident or investigation the company can show what preventive measures it took.
- What you get
- A map of contract terms to compliance obligations, and an evidence-preservation procedure for incidents and investigations.
Clear rules for employee data, joining and leaving, and AI use
- Your concern
- Employee data across subsidiaries, confidential information leaving with departing staff, staff use of generative AI and AI hiring tools all involve data protection and labour law.
- Our approach
- We build data protection, trade-secret protection, integrity training and AI-use rules into joining, employment and leaving processes, with auditable records.
- What you get
- A map of controls and records for each stage of the employee lifecycle, plus rules and training for staff AI use.
Six certification services × two trusted supply chain lines
Foundation work starts with a certificate; advanced work links certificates into the product evidence EU and US markets require. One team plans both together.
Client stories
All case studiesNamed cases are published with client permission. Other named clients published with their permission: MediaTek (trade secret protection), MPI Corporation (ISO 27001 and trade secret protection), InfoLight (ISO 27001), and the Joint Credit Information Center (JCIC) and Lativ (personal data protection). Other engagements in semiconductors, financial services, retail, automotive and conglomerates are shown by industry under NDA.
One system for every requirement your international customers raise
Customers and boards ask for more and more, but the evidence largely overlaps. Winners plans it once so one system and one body of evidence answer them all.
EU Trusted Supply Chain Integration
1 services, answered by one system
By industry
The same requirement means different things in different industries. The table shows the services each industry typically needs together.
| Industry | Foundation | International standard certification | Advanced | Trusted supply chain | ||||||
|---|---|---|---|---|---|---|---|---|
| Enterprise Risk Management (ERM) | AI Governance & Compliance | Trade Secrets & Innovation Management | Personal Data Protection (PIMS) | Business Continuity Management (BCM) | Automotive Cybersecurity | EU Trusted Supply Chain Integration | US Trusted Supply Chain | |
| Semiconductor supply chain | — | — | ||||||
| Listed companies operating globally | — | — | — | — | ||||
| AI supply chain & digital transformation | — | |||||||
| Automotive supply chain | — | — | — | — | — | — | — | |
| Smart healthcare supply chain | — | — | — | — | — | |||
| EU market supply chain | — | — | — | — | — | — | ||
The two key dates of 2027
Track regulatory change in Taiwan and abroad
Our on-premises AI intelligence system monitors regulators and standards bodies in the EU, US, Japan and Taiwan, with the original source and the impact on Taiwanese companies for every item.
Insights
All articlesOur consultants’ reading of international regulations and standards, with practical advice for Taiwanese companies.
Consultants build the system; Ahura keeps it running
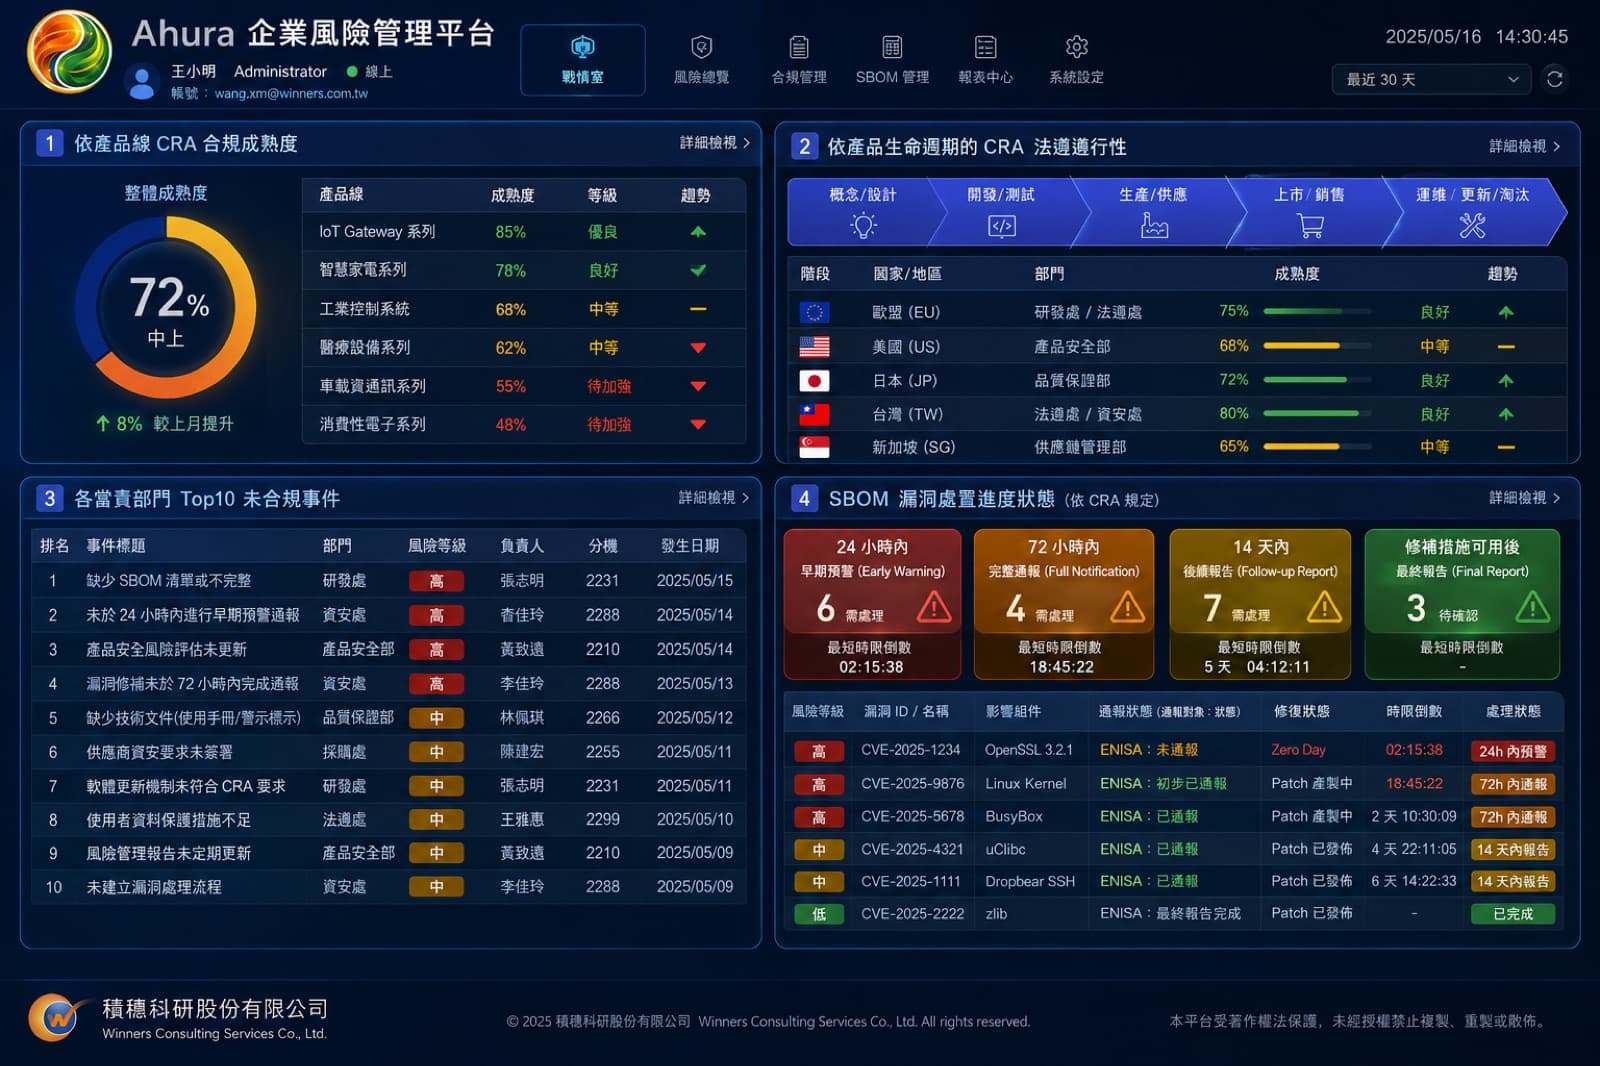
After the engagement, whether the system runs day to day decides your next audit. The Ahura platform keeps requirements, evidence and reporting workflows in one place.
From diagnostic to certification
- Free diagnosticScheduled within one working day to clarify requirements and gaps
- Tailored planRoute, timeline and fees, stating what is and is not included
- End-to-end guidanceVP- and director-level consultants attend every meeting to build the system, train staff and prepare evidence
- Certification and operationSupport for the certification audit, then ongoing operation on Ahura
Consultant qualifications
- ISO 27001/27701 Lead Auditor
- ISO 22301 Lead Auditor
- ISO 42001 AI Management System Lead Auditor
- ISO 56001 Innovation Management Lead Auditor
- COSO ERM specialist
- Academic partnership with NTUST
Winners advises. Lead Auditor qualifications mean our consultants know what certification audits look for; audits are carried out by independent certification bodies.
Frequently asked questions
All FAQWhat do I need to prepare for the free diagnostic?
After you submit the form, a consultant will hold the diagnostic with you within one working day to understand your current state and gaps, and explain applicable requirements, priorities and evidence that can be shared.
Is Winners a certification body?
No. Winners is a consultancy that helps companies build systems and prepare evidence; certification audits are carried out by independent certification bodies. Our consultants hold ISO Lead Auditor qualifications and know what audits look for.
Can several services run together?
Yes. Evidence such as risk assessment, access control, incident reporting and supplier management overlaps heavily, so planning it with one team avoids building things twice.
How do the EU CSA 2.0 and US chip controls affect Taiwanese suppliers?
Both push trust requirements down the supply chain. The EU CSA 2.0 proposal would allow high-risk suppliers to be excluded from procurement of key ICT assets, while the US uses export controls and remote-access rules to govern where advanced chips go. Taiwanese suppliers need evidence of product security and of where products come from and where they go, and Winners helps build that evidence on NIST and ISO standards.